210-255 Practice Questions
Prepare for 210-255 with more than an answer.
Unlock the full exam and previous versions
- v1Standard 313 questions Locked
- 210-250Legacy Cyber Ops Understanding Cisco Cybersecurity Fundamentals (SECFND) 220 questions Locked
- 210-255Legacy Implementing Cisco Cybersecurity Operations (SECOPS) 207 questions Current
- Exam fee
- $300 USD
- Level
- Associate
- Valid for
- 3 years
Domains covered on the exam 5
- Endpoint Threat Analysis and Computer Forensics15%
- Network Intrusion Analysis22%
- Incident Response18%
- Data and Event Analysis23%
- Incident Handling22%
- 1
Which part of the following Snort rule is the 'Rule Header'?
alert tcp $EXTERNAL_NET any -> $HTTP_SERVERS 80 (msg:"WEB-MISC"; content:"/admin.php"; sid:1000001;)Show answer details
Correct answer: A
The rule header contains the action (alert), protocol (tcp), source IP/Port ($EXTERNAL_NET any), direction operator (->), and destination IP/Port ($HTTP_SERVERS 80). The part in parentheses is the Rule Options.
- 2
In NetFlow v9 and IPFIX, the mechanism that defines the format of the exported data records, allowing for flexibility and extensibility by transmitting field definitions before data, is called a ______.
Show answer details
Correct answer: C
NetFlow v9 and IPFIX use Templates to define the structure of the flow data. The exporter sends a template record to the collector, describing the fields (like Source IP, Bytes, Packets) that will be in subsequent data records.
- 3
You need to filter Wireshark traffic to show only packets originating from IP address 192.168.1.50 destined for port 443. Which display filter is correct?
Show answer details
Correct answer: C
In Wireshark display filters,
ip.srcspecifies source IP andtcp.dstportspecifies destination TCP port. The&&operator acts as a logical AND. - 4
Which of the following statements correctly distinguish an Intrusion Prevention System (IPS) from an Intrusion Detection System (IDS)? (Select TWO)
Show answer details
Correct answer: A, C
Because it is inline, an IPS can take active measures like dropping packets, resetting connections, or blocking IPs. An IDS can only alert.
IPS devices sit inline (in the data path) to be able to drop packets and block attacks in real-time. IDS devices are typically deployed out-of-band (promiscuous mode) via a span port.
- 5
An analyst is writing a regular expression (regex) to identify potential Visa credit card numbers in a log file. Visa numbers start with 4 and are 13 or 16 digits long. Which regex pattern best matches a 16-digit Visa number?
Show answer details
Correct answer: B
^ matches start of string, 4 matches the literal '4', [0-9]{15} matches exactly 15 more digits (total 16), and $ matches end of string.
- 6
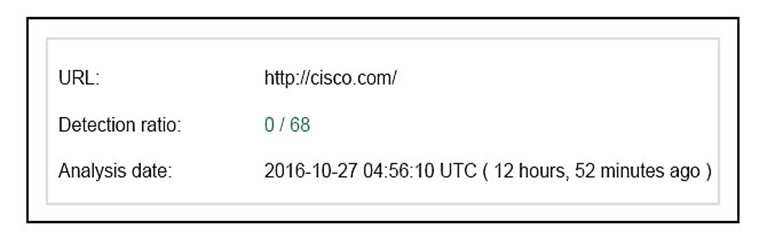
Refer to the exhibit. We have performed a malware detection on the Cisco website. Which statement about the result is true? A.The website has been marked benign on all 68 checks.B.The threat detection needs to run again.C.The website has 68 open threats.D.The website has been marked benign on 0 checks.
Show answer details
Correct answer: A
- 7
During which phase of the forensic process is data that is related to a specific event labeled and recorded to preserve its integrity? A.collectionB.examinationC.reportingD.investigation
Show answer details
Correct answer: A
- 8
Refer to the exhibit. A customer reports that they cannot access your organization's website. Which option is a possible reason that the customer cannot access the website? A.The server at 10.33.1.5 is using up too much bandwidth causing a denial-of-service.B.The server at 10.67.10.5 has a virus.C.A vulnerability scanner has shown that 10.67.10.5 has been compromised.D.Web traffic sent from 10.67.10.5 has been identified as malicious by Internet sensors.
Show answer details
Correct answer: D
