312-50v10 Certified Ethical Hacker (CEH v10) Practice Questions
Prepare for 312-50v10 with more than an answer.
Unlock the full exam and previous versions
- v1Version 1 320 questions Locked
- 312-50v10Legacy Certified Ethical Hacker (CEH v10) 321 questions Current
- 312-50v11Legacy Certified Ethical Hacker (CEH v11) 124 questions Locked
- 312-50v9Legacy Certified Ethical Hacker (CEH v9) 613 questions Locked
- 312-50v9-1349Legacy Certified Ethical Hacker (CEH v9 ext.) 803 questions Locked
- 1
What is the purpose of a demilitarized zone on a network?
Show answer details
Correct answer: B
A demilitarized zone (DMZ) provides controlled access to public-facing services while protecting the internal network. It acts as a buffer zone where external users can access specific services (like web servers) without having direct access to internal network resources, effectively isolating and securing the internal network from external threats.
- 2
You need to deploy a new web-based software package for your organization. The package requires three separate servers and needs to be available on the Internet. What is the recommended architecture in terms of server placement?
Show answer details
Correct answer: B
The recommended architecture is to place the web server in a DMZ facing the Internet, while keeping the application and database servers on the internal network. This three-tier architecture provides security by limiting external exposure while allowing the necessary communication between tiers through controlled firewall rules.
- 3
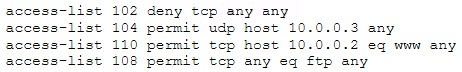
The security administrator of ABC needs to permit Internet traffic in the host 10.0.0.2 and UDP traffic in the host 10.0.0.3. He also needs to permit all FTP traffic to the rest of the network and deny all other traffic. After he applied his ACL configuration in the router, nobody can access to the ftp, and the permitted hosts cannot access the Internet. According to the next configuration, what is happening in the network?
Show answer details
Correct answer: D
In Access Control Lists (ACLs), rules are processed in order from top to bottom. The first ACL rule is denying all TCP traffic, which means subsequent ACL rules permitting specific traffic will be ignored since the deny rule is matched first. ACL rules must be ordered properly with more specific rules before general deny rules.
- 4
When conducting a penetration test, it is crucial to use all means to get all available information about the target network. One of the ways to do that is by sniffing the network. Which of the following cannot be performed by the passive network sniffing?
Show answer details
Correct answer: B
Passive network sniffing can only monitor and capture existing network traffic without interfering with it. Modifying and replaying captured network traffic requires active techniques that involve injecting or altering packets on the network, which goes beyond the capabilities of passive sniffing methods.
- 5
A company's Web development team has become aware of a certain type of security vulnerability in their Web software. To mitigate the possibility of this vulnerability being exploited, the team wants to modify the software requirements to disallow users from entering HTML as input into their Web application. What kind of Web application vulnerability likely exists in their software?
Show answer details
Correct answer: A
Cross-site scripting (XSS) vulnerabilities are mitigated by disallowing users from entering HTML tags and script code in web forms. Input validation and output encoding prevent malicious scripts from being executed in users' browsers, which is the primary attack vector for XSS attacks.
- 6
An unauthorized individual enters a building following an employee through the employee entrance after the lunch rush. What type of breach has the individual just performed?
Show answer details
Correct answer: B
Tailgating is the practice of following an authorized person through a secured entrance without proper authorization. This occurs when an unauthorized individual gains physical access by closely following an employee through security doors or checkpoints. Reverse Social Engineering involves manipulating someone to contact the attacker, Piggybacking typically involves the authorized person being aware and allowing access, and "Announced" is not a recognized security breach type. Tailgating is a common physical security threat that organizations must address through security awareness training and access controls.
- 7
Which of the following is the best countermeasure to encrypting ransomwares?
Show answer details
Correct answer: B
Keeping offline backup generations is the most effective countermeasure against ransomware because the backups are not connected to the network and cannot be encrypted by ransomware. This allows organizations to restore data without paying the ransom, as the offline backups remain unaffected by the attack.
- 8
If an attacker uses the command SELECT*FROM user WHERE name = ‘x’ AND userid IS NULL; -‘; which type of SQL injection attack is the attacker performing?
Show answer details
Correct answer: A
The double dash (--) at the end of the SQL query indicates an End of Line Comment attack. This technique comments out the rest of the original query, allowing the attacker to bypass authentication or other security checks by making the database ignore the remaining conditions in the WHERE clause.
- 9
Sophia travels a lot and worries that her laptop containing confidential documents might be stolen. What is the best protection that will work for her?
Show answer details
Correct answer: A
Full disk encryption is the best protection for confidential documents on a laptop that might be stolen. It encrypts the entire hard drive, making all data unreadable without the encryption key, even if the physical device is compromised. BIOS passwords and hidden folders can be easily bypassed by attackers with physical access.
- 10
An attacker has installed a RAT on a host. The attacker wants to ensure that when a user attempts to go to "www.MyPersonalBank.com", that the user is directed to a phishing site. Which file does the attacker need to modify?
Show answer details
Correct answer: D
The hosts file contains hostname-to-IP address mappings that override DNS lookups. By modifying this file, an attacker can redirect traffic from legitimate sites like "www.MyPersonalBank.com" to malicious phishing sites by mapping the legitimate domain to a malicious IP address.
