AZ-303 Practice Questions
Prepare for AZ-303 with more than an answer.
Unlock the full exam and previous versions
- v1Version 1 205 questions Locked
- AZ-303Legacy Microsoft Azure Architect Technologies 158 questions Current
- 1
A company needs to deploy 5 Virtual Machines. Below are the requirements for the Virtual Machines Each Virtual Machine needs to have a Private IP address Each Virtual Machine needs to have a Public IP address The same inbound and outbound security group rules.
What is the minimum number of Network Security Groups required for this requirement?Show answer details
Correct answer: A
Explanation: You can associate a Network Security Group with multiple network interfaces as shown below:Sdemovm-nsg - Network interfacesNetwork security group)ESearch (Ctrl*/)@ Overview+ AssociateI /0 ^eorch network interfacesB Activity logNAMEPUBLICIPADDRESSPRIVATEIPADDRESSVIRTUALMACHINEiS Access control (IAM)demovm98552.151.103.14310.0.0.4demovm? Tagssecondary10.0.0.5demovmX Diagnose and solve problemsSettingso-,= Inbound security rules;= Outbound security rules\ 0P Network interfacesHence since both the Inbound and Outbound network security rules are the same, we can just have one Network Security Group overall for all of the network interfaces. -- Reference: https://docs.microsoft.com/en-us/azure/virtual-network/manage-network-security-group
- 2
A company is preparing their Azure environment for the backup of their Azure Virtual Machines. They need to ensure the following when it comes to the backup of the Virtual Machines:- The Virtual machines need to be backed up daily at 03:00 UTC time- The backups should be retained for a period of 90 daysWhich of the following should you configure in Azure Recovery Services vault?
Show answer details
Correct answer: A
Explanation: To specify the backup schedule, you first need to go to the Azure Site Recovery Services vault, go to Backup policies
- 3
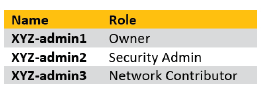
A company currently has an Azure Subscription and a tenant defined. They have a Virtual Network named as “XYZ-net" defined in Azure. They also have the following users defined in Azure AD:
Which of the following user/users would be able to assign a user the reader role to the Virtual Network “XYZ-net"?
Show answer details
Correct answer: A, E
Explanation: The Owner has all the privileges including the privilege to manage resources as shown below in the Microsoft documentation.
OwnerDescriptionLets you manage everything, including access to resources.
Id8e3af657-a8ff-443c-a75c-2fe8c4bcb635The Network Contributor role cannot assign permissions as highlighted below.
Network Contributor ^DescriptionLets you manage network , but not access to them.
Id4d97b98b-1d4f-4787-a291 -c67834d212e7ActionsMicrosoft.
Authorization/*/readRead roles and role AssignmentsMicrosoft.lnsights/alertRules/*Create and manage alert rulesMicrosoft.
Network/*M icrosoft.
Resou rceHealth/availabil ityStatuses/readCreate and manage networksGets the availability statuses for all resources in the specified scope -- Reference: httDs://docs.microsoft.com/en-us/azure/role-based-access-control/built-in-rolesExplanation: The Owner has all the privileges including the privilege to manage resources as shown below in the Microsoft documentation.
OwnerDescriptionLets you manage everything, including access to resources.
Id8e3af657-a8ff-443c-a75c-2fe8c4bcb635The Network Contributor role cannot assign permissions as highlighted below.
Network Contributor ^DescriptionLets you manage network , but not access to them.
Id4d97b98b-1d4f-4787-a291 -c67834d212e7ActionsMicrosoft.
Authorization/*/readRead roles and role AssignmentsMicrosoft.lnsights/alertRules/*Create and manage alert rulesMicrosoft.
Network/*M icrosoft.
Resou rceHealth/availabil ityStatuses/readCreate and manage networksGets the availability statuses for all resources in the specified scope -- Reference: httDs://docs.microsoft.com/en-us/azure/role-based-access-control/built-in-roles - 4
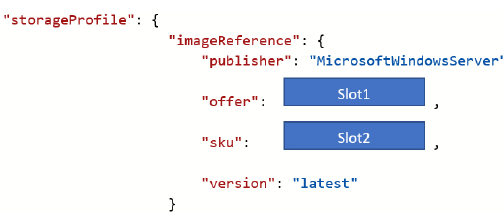
A company is planning on deploying 15 virtual machines using Azure Resource Managertemplates. All of the virtual machines should run the latest version ofWindows Server 2016. You have to complete the below storageProfile section of the template
Which of the following would go into Slot1?
Show answer details
Correct answer: B
Explanation: If you look at the Export Template section for a resource group that has a Windows Server 2016 Virtual machine deployed, you can see that values that go into the offer and Sku section
- 5
Your company has an Active directory forest named XYZ.com. The forest contains two child domains staging.
XYZ.com and production.
XYZ.com. Your company has now setup an Azure AD tenant named XYZ.com. Al of the on-premises user accounts are now being synched onto Azure AD with the help ofAzure AD Connect. The company has also implemented seamless single sign-on. You now have to change the source of authority for all user accounts in the staging.
XYZ.com domain. You have to prevent the synchronization of the staging.
XYZ.com domain. You decide to use the Azure AD Connect wizard.
Would this fulfil the requirement?Show answer details
Correct answer: A
Explanation: Yes, you can also use the Azure AD Connect wizard. This is also mentioned in the Microsoft documentation:Select the domains to be synchronized using the Azure AD Connect wizardTo set the domain filter, do the following steps:1.
Start the Azure AD Connect wizard.2.
Click Configure.3.
Select Customize Synchronization Options and click Next.4.
Enter your Azure AD credentials.5.
On the Connected Directories screen click Next.6.
On the Domain and OU filtering page click Refresh. New domains will now appear and deleted domains will disappear.^ Microsoft Azure Active Directory ConnectXWelcomeTasksConnect to Azure ADSyncConnect DirectoriesDomain/OU FilteringOptional FeaturesConfigureDomain and OU filteringIf you change the OU-filtering configuj3tiQnJEDj^jy^enjcUmctQ|^Jhyyx^ync cycle will automatically perform full import on the directory.
Directory: | corp.contoso.comO Sync all domains and OUs @i,Sync selected domains and^^^) 0 Organization) n Program DataNEW DOMAINPermissions must be granted to the synchronization account (eu.contoso.com VMSQL_f03b6b776806) for this domain before including it in your synchronization scope.® -- Reference: httDs://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-configu re-fi ltering - 6
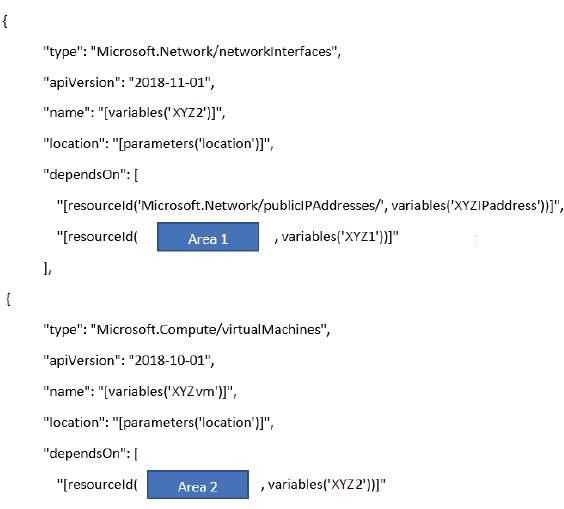
You have to deploy an Azure virtual machine using an Azure Resource Manager template. Below are snippets of the template. You have to complete the definition of the template:
Which of the following would go into Area 2?
Show answer details
Correct answer: C
Explanation: Here we have to mention the dependency on the virtual network interface When you implement an ARM template forthe deployment of the virtual machine, this dependency is evident.
- 7
You have a set of virtual machines that are hosting mission-critical applications. You have to ensure the virtual machines experience as little downtime as possible.
Which of the following can you use to maintain application availability when an Azure datacenter fails?Show answer details
Correct answer: C
Explanation: You can use Availability zones to help protect against datacenter level failures. The Microsoft documentation mentions the following:Availability ZonesAn Availability Zone is a high-availability offering that protects your applications and data from datacenter failures. Availability Zones are unique physical locations within an Azure region. Each zone is made up ofone or more datacenters equipped with independent power, cooling, and networking. To ensure resiliency, there's a minimum ofthree separate zones in all enabled regions. The physical separation ofAvailability Zones within a region protects applications and data from datacenter failures. Zone-redundant services replicate your applications and data across Availability Zones to protect from single-points-of-failure. With Availability Zones, Azure offers industry best 99.99% VM uptime SLA. The full Azure SLA explains the guaranteed availability ofAzure as a whole.
An Availability Zone in an Azure region is a combination of a fault domain and an update domain. For example, if you create three or more VMs across three zones in an Azure region, your VMs are effectively distributed across three fault domains and three update domains. The Azure platform recognizes this distribution across update domains to make sure that VMs in different zones are not scheduled to be updated at the same time.
Since this is clearly given in the Microsoft documentation, all other options are incorrect -- Reference: https://docs.microsoft.com/en-us/azu re/ava ilab i I ity-zones/az-overview - 8
A company wants to sync their on-premise AD with Azure A
Show answer details
Correct answer: C
Explanation: This issue is also mentioned in the Microsoft documentation.
Staging modeStaging mode can be used for several scenarios, including:•
High availability.•
Test and deploy new configuration changes.•
Introduce a new server and decommission the old.
During installation, you can select the server to be in staging mode. This action makes the server active for import and synchronization, but it does not run any exports. A server in staging mode is not running password sync or password writeback, even ifyou selected these features during installation. When you disable staging mode, the server starts exporting, enables password sync, and enables password writeback.
Since this is clearly mentioned in the documentation, all other options are incorrect -- Reference: httDs://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-staging-serverIt - 9
A company has setup the following Azure Virtual Machines in Azure:
There is a requirement to setup a load balancer in Azure and ensure the Virtual Machines are placed behind the load balancer. It needs to be ensured that session affinity is in place for requests flowing via the Load balancer.
In which of the following section of the Load balancerwould you define this?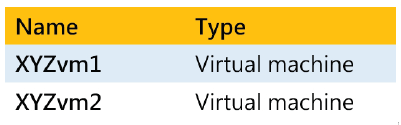
Show answer details
Correct answer: C
Explanation: You will define this in the load balancing rule as shown below:Add load balancing rule? X* Namedemo* IP Version® IPv4 O IPv6* Frontend IP address eI 51.140.87.135 (LoadBalancerFrontEnd)Protocol®TCP QUDP* PortI 80* Backend portFsoBackend pool eI demopool (1 virtual machine7Health probedemoprobe (TCP:80))Session persistence 6NoneNoneClient IPClient IP and protocolFloating lP (direct server retur
- 10
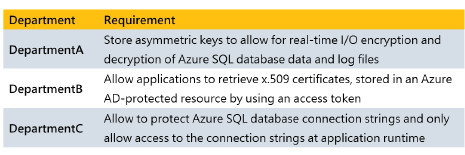
Your company needs to deploy resources for several departments. These resources will reside in Azure. Each department has a separate requirement when it comes to security.
Which of the following would you use to fulfil the requirement for DepartmentA?
Show answer details
Correct answer: C
Explanation: You can use the Azure Key vault service for the storage of encryption keys The Microsoft documentation mentions the following:About Azure Key VaultAzure Key Vault helps solve the following problems:•
Secrets Management - Azure Key Vault can be used to Securely store and tightly control access to tokens, passwords, certificates, API keys, and other secrets•
Key Management - Azure Key Vault can also be used as a Key Management solution. Azure Key Vault makes it easy to create and control the encryption keys used to encrypt your data.•
Certificate Management - Azure Key Vault is also a service that lets you easily provision, manage, and deploy public and private Transport Layer Security/Secure Sockets Layer (TLS/SSL) certificates for use with Azure and your internal connected resources.•
Store secrets backed by Hardware Security Modules - The secrets and keys can be protected either by software or FIPS 140-2 Level 2 validated HSMsSince this is clearly given in the Microsoft documentation, all other options are incorrect -- Reference: https://docs.microsoft.com/en-us/azure/key-vault/general/overview
