PCNE Practice Questions
Prepare for PCNE with more than an answer.
Unlock the full exam and previous versions
- v1Google Cloud Professional Cloud Network Engineer 153 questions Locked
- PCNELegacy Professional Cloud Network Engineer 308 questions Current
- 1
You want to configure a NAT to perform address translation between your on-premises network blocks and GCP.
Which NAT solution should you use?
Show answer details
Correct answer: A
Reference: https://cloud.google.com/nat/docs/overview
- 2
You need to restrict access to your Google Cloud load-balanced application so that only specific IP addresses can connect.
What should you do?
Show answer details
Correct answer: C
Reference: https://link.springer.eom/chapter/10.1007/978-1 -4842-1004-8 4
- 3
You decide to set up Cloud NAT. After completing the configuration, you find that one of your instances is not using the Cloud NAT for outbound NAT.
What is the most likely cause of this problem?
Show answer details
Correct answer: B
- 4
You have recently been put in charge of managing identity and access management for your organization. You have several projects and want to use scripting and automation wherever possible. You want to grant the editor role to a project member.
Which two methods can you use to accomplish this? (Choose two.)
Show answer details
Correct answer: D, E
D, E -- Reference: https://cloud.qooqle.com/iam/docs/qrantinq-chanqinq-revokinq-access
D, E -- Reference: https://cloud.qooqle.com/iam/docs/qrantinq-chanqinq-revokinq-access
- 5
A DevOps team needs to deploy a fleet of third-party security appliances as Network Virtual Appliances (NVAs) to inspect all traffic between a 'webapp' subnet and a 'database' subnet within the same VPC. You must ensure high availability for the inspection service. Which configuration should you implement?
graph TD subgraph VPC subgraph WebApp Subnet WebAppVM[Web App VM] end subgraph NVA Subnet ILB[Internal TCP/UDP LB] NVA1[NVA Instance 1] NVA2[NVA Instance 2] ILB --> NVA1 ILB --> NVA2 end subgraph Database Subnet DBVM[Database VM] end end WebAppVM -- Route --> ILB -- Inspected --> DBVMShow answer details
Correct answer: C
This is the correct Google-recommended practice for creating highly available NVA deployments. Using an Internal TCP/UDP Load Balancer allows traffic to be distributed across multiple healthy NVA instances. Setting the load balancer's forwarding rule as the next hop for a custom route ensures that traffic is automatically redirected if one of the NVAs fails its health check, providing seamless failover and high availability.
- 6
You need to establish network connectivity between three Virtual Private Cloud networks, Sales, Marketing, and Finance, so that users can access resources in all three VPCs. You configure VPC peering between the Sales VPC and the Finance VPC. You also configure VPC peering between the Marketing VPC and the Finance VPC. After you complete the configuration, some users cannot connect to resources in the Sales VPC and the Marketing VPC. You want to resolve the problem.
What should you do?
Show answer details
Correct answer: A
A
- 7
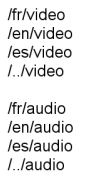
Your company’s Google Cloud-deployed, streaming application supports multiple languages. The application development team has asked you how they should support splitting audio and video traffic to different backend Google Cloud storage buckets. They want to use URL maps and minimize operational overhead. They are currently using the following directory structure:
Which solution should you recommend?
Show answer details
Correct answer: D
D
- 8
You want to deploy a VPN Gateway to connect your on-premises network to GCP. You are using a non BGP-capable on-premises VPN device. You want to minimize downtime and operational overhead when your network grows. The device supports only IKEv2, and you want to follow Google-recommended practices.
What should you do?
Show answer details
Correct answer: D
- 9
You are disabling DNSSEC for one of your Cloud DNS-managed zones. You removed the DS records from your zone file, waited for them to expire from the cache, and disabled DNSSEC for the zone. You receive reports that DNSSEC validating resolves are unable to resolve names in your zone.
What should you do?
Show answer details
Correct answer: C
Explanation:
Before disabling DNSSEC for a managed zone you want to use, you must deactivate DNSSEC at your domain registrar to ensure that DNSSEC-validating resolvers can still resolve names in the zone. -- Reference: https://cloud.google.com/dns/docs/dnssec-config - 10
Your on-premises data center has 2 routers connected to your GCP through a VPN on each router. All applications are working correctly; however, all of the traffic is passing across a single VPN instead of being load- balanced across the 2 connections as desired.
During troubleshooting you find:
• Each on-premises router is configured with the same ASN.
• Each on-premises router is configured with the same routes and priorities.
• Both on-premises routers are configured with a VPN connected to a single Cloud Router.
• The VPN logs have no-proposal-chosen lines when the VPNs are connecting.
• BGP session is not established between one on-premises router and the Cloud Router.What is the most likely cause of this problem?
Show answer details
Correct answer: C
C
