AWS Certified Security - Specialty Practice Questions
Prepare for SCS-C01 with more than an answer.
Unlock the full exam and previous versions
- v1AWS Certified Security - Speciality 275 questions Locked
- SCS-C01Legacy AWS Certified Security - Specialty 223 questions Current
- SCS-C02Legacy AWS Certified Security - Specialty 71 questions Locked
- 1
A company wants to deploy an application in a private VPC that will not be connected to the internet. The company’s security team will not allow bastion hosts or methods using SSH to log in to Amazon EC2 instances. The application team plans to use AWS Systems Manager Session Manager to connect to and manage the EC2 instances.
Which combination of steps should the security team take? (Choose three.)
Show answer details
Correct answer: A, B, E
A, B, E -- Reference: httDs://aws.amazon.com/blogs/mt/replacing-a-bastion-host-with-amazon-ec2-systems-manager/
A, B, E -- Reference: httDs://aws.amazon.com/blogs/mt/replacing-a-bastion-host-with-amazon-ec2-systems-manager/
A, B, E -- Reference: httDs://aws.amazon.com/blogs/mt/replacing-a-bastion-host-with-amazon-ec2-systems-manager/
- 2
A company is using AWS Organizations to manage multiple AWS accounts. The company has an application that allows users to assume the AppUser 1AM role to download files from an Amazon S3 bucket that is encrypted with an AWS KMS CMK. However, when users try to access the files in the S3 bucket, they get an access denied error.
What should a security engineer do to troubleshoot this error? (Choose three.)
Show answer details
Correct answer: B, D, E
B, D, E
B, D, E
B, D, E
- 3
A company has hundreds of AWS accounts, and a centralized Amazon S3 bucket used to collect AWS CloudTrail logs for all of these accounts. A Security Engineer wants to create a solution that will enable the company to run ad hoc queries against its CloudTrail logs dating back 3 years from when the trails were first enabled in the company’s AWS account.
How should the company accomplish this with the least amount of administrative overhead?
Show answer details
Correct answer: B
B
- 4
An organization wants to log all AWS API calls made within all of its AWS accounts, and must have a central place to analyze these logs.
What steps should be taken to meet these requirements in the MOST secure manner? (Choose two.)
Show answer details
Correct answer: B, E
B, E
B, E
- 5
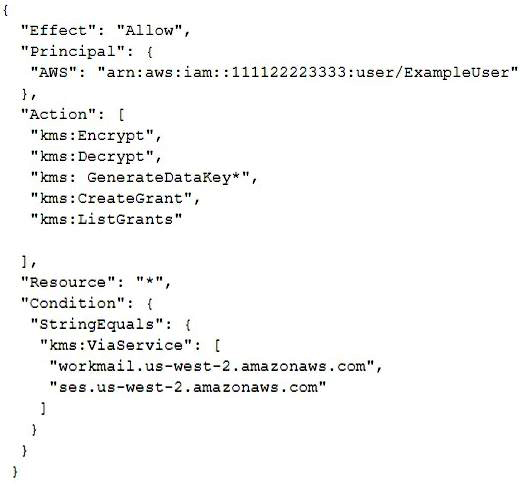
What is the function of the following AWS Key Management Service (KMS) key policy attached to a customer master key (CMK)?
Show answer details
Correct answer: C
- 6
Developers in an organization have moved from a standard application deployment to containers. The Security Engineer is tasked with ensuring that containers are secure.
Which strategies will reduce the attack surface and enhance the security of the containers? (Choose two.)
Show answer details
Correct answer: B, D
B, D
B, D
- 7
During a recent internal investigation, it was discovered that all API logging was disabled in a production account, and the root user had created new API keys that appear to have been used several times.
What could have been done to detect and automatically remediate the incident?Show answer details
Correct answer: C
C
- 8
A Security Administrator has a website hosted in Amazon S3. The Administrator has been given the following requirements:
. Users may access the website by using an Amazon CloudFront distribution.
. Users may not access the website directly by using an Amazon S3 URL.Which configurations will support these requirements? (Choose two.)
Show answer details
Correct answer: A, C
A, C
A, C
- 9
A company has a forensic logging use case whereby several hundred applications running on Docker on EC2 need to send logs to a central location. The Security Engineer must create a logging solution that is able to perform real-time analytics on the log files, grants the ability to replay events, and persists data.
Which AWS Services, together, can satisfy this use case? (Choose two.)
Show answer details
Correct answer: B, D
B, D
B, D
- 10
A Security Engineer is implementing a solution to allow users to seamlessly encrypt Amazon S3 objects without having to touch the keys directly. The solution must be highly scalable without requiring continual management. Additionally, the organization must be able to immediately delete the encryption keys.
Which solution meets these requirements?
Show answer details
Correct answer: B
B