SecurityX (Extended) Practice Questions
Prepare for CA1-005 with more than an answer.
Unlock the full exam and previous versions
- v1Version 1 210 questions Locked
- CA1-005Legacy CompTIA SecurityX (Extended) 215 questions Current
- CAS-003Legacy CompTIA Advanced Security Practitioner (CASP) 361 questions Locked
- CAS-004Legacy Comptia Advanced Security Practitioner (casp+) 149 questions Locked
- Exam fee
- $400 USD
- Level
- Expert
- Valid for
- 3 years
Domains covered on the exam 4
- Governance, Risk, and Compliance20%
- Security Architecture27%
- Security Engineering31%
- Security Operations22%
- 1
A security engineer is designing a logging and monitoring solution for a serverless application built with AWS Lambda and API Gateway. The requirements are to centralize application and execution logs, enable real-time analysis of error rates, and create automated alerts for specific security events (e.g., a sudden spike in 4xx error codes). Which combination of AWS services would be the MOST effective and integrated solution to meet these requirements?
Show answer details
Correct answer: B
This is the most integrated and standard solution for serverless monitoring on AWS. AWS Lambda and API Gateway natively send logs to CloudWatch Logs for centralization. From there, Metric Filters can be created to extract data points (like error counts) and publish them as CloudWatch Metrics for real-time analysis. Finally, CloudWatch Alarms can be configured to monitor these metrics and trigger automated actions (like sending an SNS notification) when a threshold is breached, meeting all the requirements.
- 2
During an incident response, an analyst discovers that an attacker has gained access to a DevOps engineer's credentials and is attempting to alter the CI/CD pipeline. The goal is to insert malicious code into a container image during the build process. Which of the following security controls would be MOST effective at preventing the compromised credentials from being used to push a malicious image to the container registry?
Show answer details
Correct answer: D
This is the most effective control. By configuring the container registry to only accept images that are digitally signed by a specific, trusted, and hardened CI/CD service account, any attempt to push an image using the compromised engineer's credentials will fail the signature validation. This ensures that only images built through the official, sanctioned pipeline can be stored, providing a strong guarantee of image integrity and provenance.
- 3
A security operations team has been tasked with improving its ability to detect insider threats. The team needs to identify anomalous user behavior, such as an employee accessing sensitive files they have never accessed before, logging in at unusual hours, or exfiltrating large amounts of data. The solution must integrate with Active Directory, file servers, and cloud application logs. Which security technology is specifically designed to address this requirement?
Show answer details
Correct answer: C
UEBA is the technology specifically designed for this purpose. It ingests logs from various sources (like AD, file servers, and cloud apps), uses machine learning to build a baseline of normal behavior for each user and entity, and then detects and alerts on deviations from that baseline. This allows it to effectively identify insider threats based on anomalous activities like unusual file access, login times, and data movement.
- 4
A hospital is designing a network architecture to protect its sensitive electronic health record (EHR) systems while allowing connectivity for medical IoT devices (e.g., infusion pumps, heart monitors) and guest Wi-Fi. The primary goals are to prevent lateral movement from less trusted devices to the critical EHR systems and to enforce strict access controls. Which network design principle is MOST critical to implement?
graph TD subgraph "Hospital Network" A[Internet] --> B[Firewall] B --> C{Core Switch} C --> D[Guest Wi-Fi VLAN] C --> E[Medical IoT VLAN] C --> F[EHR Systems VLAN] C --> G[Admin Workstations VLAN] end style D fill:#f9f,stroke:#333,stroke-width:2px style E fill:#f9f,stroke:#333,stroke-width:2px style F fill:#ccf,stroke:#333,stroke-width:4px style G fill:#ccf,stroke:#333,stroke-width:2pxShow answer details
Correct answer: B
Network segmentation is the most critical principle here. By placing different types of devices into separate VLANs (Guest Wi-Fi, Medical IoT, EHR Systems), the hospital can create isolated broadcast domains. Access Control Lists (ACLs) can then be applied between these VLANs to strictly control traffic flow, preventing devices on the Guest or IoT networks from communicating directly with the highly sensitive EHR systems, thus stopping lateral movement.
- 5
A GRC analyst is creating a RACI matrix for the company's new vulnerability management program to clarify roles and responsibilities. For the task 'Approve Emergency Patch Deployment,' which role should be assigned as 'Accountable'?
Show answer details
Correct answer: D
In a RACI matrix, 'Accountable' refers to the single individual who has the ultimate ownership and authority for the task's success. The Business System Owner is accountable for the risk to their system. Therefore, they have the authority to accept the risk of deploying an emergency patch (and the risk of not deploying it) and are ultimately accountable for the decision.
- 6
A company plans to implement a research facility with intellectual property data that should be protected. The following is the security diagram proposed by the security architect:Which of the following security architect models is illustrated by the diagram?
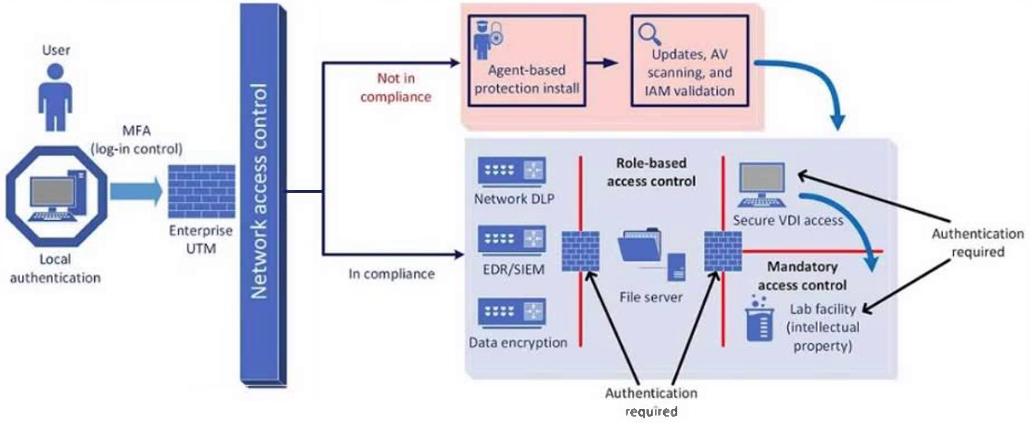
Show answer details
Correct answer: D
- 7
A financial technology firm works collaboratively with business partners in the industry to share threat intelligence within a central platform. This collaboration gives partner organizations the ability to obtain and share data associated with emerging threats from a variety of adversaries. Which of the following should the organization most likely leverage to facilitate this activity? (Choose two.) A.CWPPB.YARAC.ATT&CKD.STIXE.TAXIIF.JTAG
Show answer details
Correct answer: D, E
- 8
During a gap assessment, an organization notes that BYOD usage is a significant risk. The organization implemented administrative policies prohibiting BYOD usage. However, the organization has not implemented technical controls to prevent the unauthorized use of BYOD assets when accessing the organization's resources. Which of the following solutions should the organization implement to best reduce the risk of BYOD devices? (Choose two.) A.Cloud IAM, to enforce the use of token-based MFAB.Conditional access, to enforce user-to-device bindingC.NAC, to enforce device configuration requirementsD.PAM, to enforce local password policiesE.SD-WAN, to enforce web content filtering through external proxiesF.DLP, to enforce data protection capabilities
Show answer details
Correct answer: B, C
- 9
A security administrator is performing a gap assessment against a specific OS benchmark. The benchmark requires the following configurations be applied to endpoints:• Full disk encryption• Host-based firewall• Time synchronization• Password policies• Application allow listing• Zero Trust application accessWhich of the following solutions best addresses the requirements? (Choose two.)
Show answer details
Correct answer: A, D
- 10
A global organization is reviewing potential vendors to outsource a critical payroll function. Each vendor's plan includes using local resources in multiple regions to ensure compliance with all regulations. The organization's Chief Information Security Officer is conducting a risk assessment on the potential outsourcing vendors' subprocessors. Which of the following best explains the need for this risk assessment? A.Risk mitigations must be more comprehensive than the existing payroll provider.B.Due care must be exercised during all procurement activities.C.The responsibility of protecting PII remains with the organization.D.Specific regulatory requirements must be met in each jurisdiction.
Show answer details
Correct answer: C
