CS0-002 Cybersecurity Analyst (CySA+ v2) Practice Questions
Prepare for CS0-002 with more than an answer.
Unlock the full exam and previous versions
- v1CompTIA Cybersecurity Analyst (CySA+) V4 150 questions Locked
- CS0-002Legacy CompTIA Cybersecurity Analyst (CySA+ v2) 122 questions Current
- CS0-003Legacy CompTIA Cybersecurity Analyst (CySA+ v3) 271 questions Locked
- 1
A cyber-incident response analyst is investigating a suspected cryptocurrency miner on a company's server.
Which of the following is the FIRST step the analyst should take?
Show answer details
Correct answer: D
D
- 2
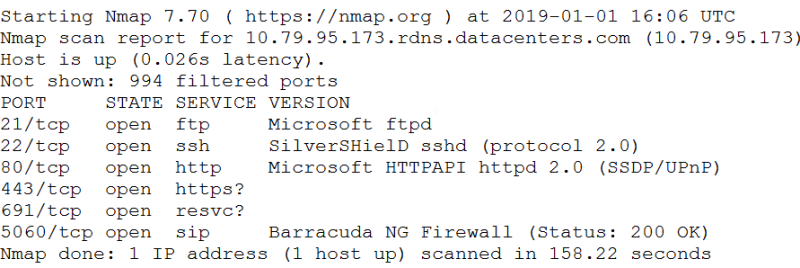
An information security analyst is compiling data from a recent penetration test and reviews the following output:
The analyst wants to obtain more information about the web-based services that are running on the target.Which of the following commands would MOST likely provide the needed information?
Show answer details
Correct answer: D
D
- 3
A compliance officer of a large organization has reviewed the firm's vendor management program but has discovered there are no controls defined to evaluate third-party risk or hardware source authenticity. The compliance officer wants to gain some level of assurance on a recurring basis regarding the implementation of controls by third parties.
Which of the following would BEST satisfy the objectives defined by the compliance officer? (Choose two.)
Show answer details
Correct answer: A, E
A,E
A,E
- 4
An analyst is performing penetration testing and vulnerability assessment activities against a new vehicle automation platform.
Which of the following is MOST likely an attack vector that is being utilized as part of the testing and assessment?
Show answer details
Correct answer: B
Explanation: IoT devices also often run real-time operating systems (RTOS). These are either special purpose operating systems or variants of standard operating systems designed to process data rapidly as it arrives from sensors or other IoT components.
- 5
An information security analyst observes anomalous behavior on the SCADA devices in a power plant. This behavior results in the industrial generators overheating and destabilizing the power supply.
Which of the following would BEST identify potential indicators of compromise?
Show answer details
Correct answer: C
C
- 6
Which of the following would MOST likely be included in the incident response procedure after a security breach of customer PII?
Show answer details
Correct answer: B
B
