SY0-501 Security+ (2020) Practice Questions
Prepare for SY0-501 with more than an answer.
Unlock the full exam and previous versions
- v1Version 1 425 questions Locked
- SY0-501Legacy Security+ (2020) 980 questions Current
- SY0-601Legacy Security+ (2021) 78 questions Locked
- 1
An organization has determined it can tolerate a maximum of three hours of downtime.
Which of the following has been specified?
Show answer details
Correct answer: A
Recovery Time Objective (RTO) defines the maximum acceptable downtime for a system or service following a disaster or disruptive event. RTO specifies how quickly systems must be restored to avoid significant business impact and is a critical metric in business continuity planning. Organizations use RTO to determine appropriate recovery strategies, resource allocation, and technology investments needed to meet recovery targets. RTO differs from RPO (Recovery Point Objective) which focuses on acceptable data loss rather than downtime duration.
- 2
Which of the following types of keys is found in a key escrow?
Show answer details
Correct answer: B
Key escrow systems store private keys to ensure authorized access to encrypted data when primary key holders are unavailable or in legal/compliance scenarios. Private keys are the sensitive cryptographic material that must be securely held in escrow because they enable decryption of protected data. Public keys are not stored in escrow as they are freely distributable, and symmetric keys are typically used for session encryption rather than long-term storage requiring escrow. Organizations use key escrow for regulatory compliance, data recovery, and law enforcement access to encrypted communications and storage systems.
- 3
An auditor wants to test the security posture of an organization by running a tool that will display the following:
Which of the following commands should be used?
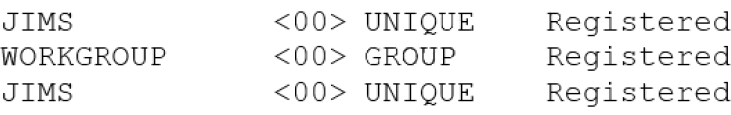
Show answer details
Correct answer: A
Based on the output shown in the image displaying NetBIOS name table information, the nbtstat command should be used. The nbtstat command displays NetBIOS over TCP/IP statistics, name table contents, and name cache information for Windows systems. The image shows typical nbtstat output with computer names, workgroups, and NetBIOS service registrations. This command is essential for network troubleshooting, security auditing, and identifying NetBIOS-enabled systems on the network. Other commands like netstat show network connections, while nslookup resolves DNS queries, but nbtstat specifically targets NetBIOS information as shown in the output.
- 4
Which of the following encryption methods does PKI typically use to securely protect keys?
Show answer details
Correct answer: C
Asymmetric encryption uses two mathematically related keys - a public key for encryption and a private key for decryption - enabling secure communication without prior key exchange. This cryptographic method solves the key distribution problem of symmetric encryption and enables digital signatures, key exchange, and secure communications between parties who have never met. Common asymmetric algorithms include RSA, ECC, and Diffie-Hellman, each providing different security properties for various use cases.
- 5
An organization is using a tool to perform a source code review.
Which of the following describes the case in which the tool incorrectly identifies the vulnerability?
Show answer details
Correct answer: C
A false positive occurs when a security system incorrectly identifies benign activity as malicious, triggering alerts for legitimate actions. False positives reduce the effectiveness of security monitoring by creating alert fatigue, wasting analyst time, and potentially causing legitimate business activities to be blocked. High false positive rates can lead to analysts ignoring alerts or disabling security controls. Proper tuning, baseline establishment, and continuous refinement are essential to minimize false positives while maintaining security effectiveness.
- 6
When performing data acquisition on a workstation, which of the following should be captured based on memory volatility? (Choose two.)
Show answer details
Correct answer: B, E
During digital forensics data acquisition, swap/pagefile and RAM should be captured first due to their high memory volatility. RAM contains the most volatile data including running processes, network connections, encryption keys, and recent user activity that disappears when power is lost. Swap/pagefile contains virtual memory data that may include passwords, encryption keys, and sensitive information temporarily stored on disk. These volatile memory sources must be captured immediately before the system is powered down, as they contain critical forensic evidence that cannot be recovered once lost.
During digital forensics data acquisition, swap/pagefile and RAM should be captured first due to their high memory volatility. RAM contains the most volatile data including running processes, network connections, encryption keys, and recent user activity that disappears when power is lost. Swap/pagefile contains virtual memory data that may include passwords, encryption keys, and sensitive information temporarily stored on disk. These volatile memory sources must be captured immediately before the system is powered down, as they contain critical forensic evidence that cannot be recovered once lost.
- 7
Which of the following would a security specialist be able to determine upon examination of a server’s certificate?
Show answer details
Correct answer: D
When examining a server certificate, security specialists can determine the Object Identifier (OID) which defines the certificate purpose and usage. The OID specifies what the certificate can be used for, such as SSL/TLS server authentication, code signing, or email encryption. The CA public key would be found in the CA certificate (not the server certificate), the server private key is never included in certificates (only the public key), and the CSR (Certificate Signing Request) is a separate document used during certificate creation, not embedded in the final certificate.
- 8
A security analyst is diagnosing an incident in which a system was compromised from an external IP address. The socket identified on the firewall was traced to 207.46.130.0:6666.
Which of the following should the security analyst do to determine if the compromised system still has an active connection?
Show answer details
Correct answer: B
The netstat command is the correct tool to determine if the compromised connection to 207.46.130.0:6666 is still active on the local system. Netstat displays active network connections, listening ports, and routing tables, allowing the analyst to see if the socket connection is still established. Tracert traces the path to a destination, ping tests connectivity, and nslookup resolves domain names to IP addresses, but none of these show active connections like netstat does.
- 9
Multiple organizations operating in the same vertical want to provide seamless wireless access fortheir employees as they visit the other organizations.
Which of the following should be implemented if all the organizations use the native 802.1x client on their mobile devices?
Show answer details
Correct answer: B
RADIUS federation is the correct solution for seamless wireless access across multiple organizations using native 802.1x clients. RADIUS federation allows organizations to establish trust relationships where employees can authenticate using their home organization credentials when visiting partner organizations. This works by federated RADIUS servers that can proxy authentication requests between trusted domains. Shibboleth, SAML, OAuth, and OpenID Connect are web-based federation protocols designed for browser applications, not native 802.1x wireless authentication which requires RADIUS infrastructure for EAP authentication protocols.
- 10
Which of the following BEST describes an important security advantage yielded by implementing vendor diversity?
Show answer details
Correct answer: C
Resiliency is the primary security advantage of implementing vendor diversity in security architectures. When organizations use multiple vendors for security solutions, they reduce single points of failure and minimize the impact of vendor-specific vulnerabilities or exploits. If one vendor solution is compromised, others remain functional, maintaining overall security posture. Sustainability refers to long-term viability, homogeneity means using similar systems (opposite of diversity), and configurability relates to customization options rather than security advantages.
- 11
In a corporation where compute utilization spikes several times a year, the Chief Information Officer (CIO) has requested a cost-effective architecture to handle the variable capacity demand.
Which of the following characteristics BEST describes what the CIO has requested?
Show answer details
Correct answer: A
Elasticity is the optimal characteristic for handling variable capacity demand with cost-effectiveness. Elasticity allows systems to automatically scale resources up during demand spikes and scale down during low usage periods, ensuring you only pay for resources actually used. This automated provisioning and de-provisioning based on current demand is ideal for organizations with periodic spikes. Scalability refers to the ability to handle increased load but doesn't necessarily include the automatic scaling down for cost savings. High availability and redundancy focus on uptime rather than cost-effective capacity management.