312-38 Certified Network Defender (CND) Practice Questions
Prepare for 312-38 with more than an answer.
- Exam fee
- $550 USD
- Level
- Professional
- Valid for
- 3 years
Domains covered on the exam 8
- Network Defense Management15%
- Network Perimeter Protection20%
- Endpoint Protection35%
- Application and Data Protection10%
- Enterprise Virtual, Cloud, and Wireless Network Protection15%
- Network Traffic Monitoring and Analysis10%
- Incident Response10%
- Incident Prediction15%
- 1
Which of the following is a protocol that describes an approach to providing "streamlined" support of OSI application services on top of TCP/IP-based networks for some constrained environments?
Show answer details
Correct answer: B
Explanation:
Lightweight Presentation Protocol (LPP) is a protocol that describes an approach to providing "streamlined" support of OSI application services on top of TCP/IP-based networks for some constrained environments. This protocol was initially derived from a requirement to run the ISO Common Management Information Protocol (CMIP) in TCP/IP-based networks.
This protocol is designed for a particular class of OSI applications, namely those entities whose application context includes only an Association Control Service Element (ACSE) and a Remote Operations Service Element (ROSE).
Answer option D is incorrect. The Dynamic Host Configuration Protocol (DHCP) is a computer networking protocol used by hosts (DHCP clients) to retrieve IP address assignments and other configuration information. DHCP uses a client-server architecture. The client sends a broadcast request for configuration information. The DHCP server receives the request and responds with configuration information from its configuration database. In the absence of DHCP, all hosts on a network must be manually configured individually - a time-consuming and often error-prone undertaking. DHCP is popular with ISP's because it allows a host to obtain a temporary IP address.
Answer option A is incorrect. Answer option C is incorrect. Internet Relay Chat (IRC) is a chat service, which is a client-server protocol that supports real-time text chat between two or more users over a TCPIP network. - 2
You are an Administrator for a network at an investment bank. You are concerned about individuals breeching your network and being able to steal data before you can detect their presence and shut down their access. Which of the following is the best way to address this issue?
Show answer details
Correct answer: C
Explanation:
A honey pot is designed to attract intruders to a false server that has no real data (but may seem to have valuable data). The specific stated purpose of a honey pot is as a backup plan in case an intruder does gain access to your network.
Answer option B is incorrect. The firewall may help reduce the chance of an intruder gaining access, but won't help protect you once they have gained access. - 3
Which of the following is the practice of sending unwanted e-mail messages, frequently with commercial content, in large quantities to an indiscriminate set of recipients? Each correct answer represents a complete solution. Choose all that apply.
Show answer details
Correct answer: A, B
A, B -- Explanation:
E-mail spam, also known as unsolicited bulk email (UBE), junk mail, or unsolicited commercial email (UCE), is the practice of sending unwanted e-mail messages, frequently with commercial content, in large quantities to an indiscriminate set of recipients.
Answer option C is incorrect. Email spoofing is a fraudulent email activity in which the sender address and other parts of the email header are altered to appear as though the email originated from a different source. Email spoofing is a technique commonly used in spam and phishing
ECCouncil 312-38 Exam
emails to hide the origin of the email message. By changing certain properties of the email, such as the From, Return-Path and Reply-To fields (which can be found in the message header), ill- intentioned users can make the email appear to be from someone other than the actual sender.
The result is that, although the email appears to come from the address indicated in the From field (found in the email headers), it actually comes from another source.
Answer option D is incorrect. Email jamming is the use of sensitive words in e-mails to jam the authorities that listen in on them by providing a form of a red herring and an intentional annoyance.
In this attack, an attacker deliberately includes "sensitive" words and phrases in otherwise innocuous emails to ensure that these are picked up by the monitoring systems. As a result, the senders of these emails will eventually be added to a "harmless" list and their emails will be no longer intercepted, hence it will allow them to regain some privacy.A, B -- Explanation:
E-mail spam, also known as unsolicited bulk email (UBE), junk mail, or unsolicited commercial email (UCE), is the practice of sending unwanted e-mail messages, frequently with commercial content, in large quantities to an indiscriminate set of recipients.
Answer option C is incorrect. Email spoofing is a fraudulent email activity in which the sender address and other parts of the email header are altered to appear as though the email originated from a different source. Email spoofing is a technique commonly used in spam and phishing
ECCouncil 312-38 Exam
emails to hide the origin of the email message. By changing certain properties of the email, such as the From, Return-Path and Reply-To fields (which can be found in the message header), ill- intentioned users can make the email appear to be from someone other than the actual sender.
The result is that, although the email appears to come from the address indicated in the From field (found in the email headers), it actually comes from another source.
Answer option D is incorrect. Email jamming is the use of sensitive words in e-mails to jam the authorities that listen in on them by providing a form of a red herring and an intentional annoyance.
In this attack, an attacker deliberately includes "sensitive" words and phrases in otherwise innocuous emails to ensure that these are picked up by the monitoring systems. As a result, the senders of these emails will eventually be added to a "harmless" list and their emails will be no longer intercepted, hence it will allow them to regain some privacy. - 4
Fill in the blank with the appropriate word. The ____________________risk analysis process analyzes the effect of a risk event deriving a numerical value.
Show answer details
Correct answer: A
Explanation:
Quantitative risk analysis is a process to assess the probability of achieving particular project objectives, to quantify the effect of risks on the whole project objective, and to prioritize the risks based on the impact to the overall project risk. The quantitative risk analysis process analyzes the effect of a risk event deriving a numerical value. It also presents a quantitative approach to build decisions in the presence of uncertainty. The inputs for quantitative risk analysis are as follows:
Organizational process assets Project scope statement Risk management plan Risk register Project management plan - 5
A retail company is deploying a new e-commerce platform. To comply with PCI-DSS, the architecture must strictly segment the public-facing web servers from the internal network containing the customer database. The web servers are in a DMZ and need to communicate with application servers on the internal network, but no traffic should ever be initiated from the DMZ to the internal network. The following diagram shows a proposed firewall ruleset for the firewall between the DMZ and the Internal Network. What is the critical security flaw in this ruleset?
graph TD subgraph Ruleset [Firewall Rules: DMZ to Internal] rule1[1. Source: DMZ, Dest: Internal_App_Server, Port: 8443, Action: Allow] rule2[2. Source: ANY, Dest: ANY, Port: ANY, Action: Deny] end subgraph Legend direction LR DMZ_Subnet[DMZ Subnet] --> rule1 Internal_App[Internal App Server] --> rule1 endShow answer details
Correct answer: C
The critical flaw is that Rule 1 allows new connections to be initiated from the DMZ to the internal network. A secure configuration would block all initiated traffic from the DMZ. Instead, a stateful firewall on the internal network edge should have a rule allowing traffic from the internal application servers to the DMZ web servers. The stateful nature of the firewall would then automatically permit the return traffic (the response from the DMZ) without needing an explicit inbound rule from the DMZ.
- 6
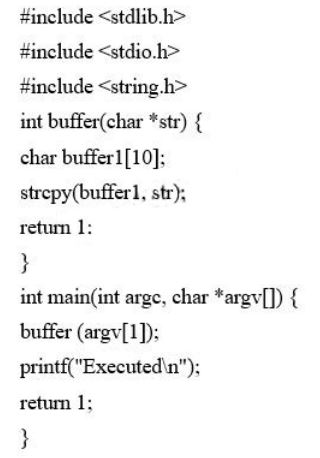
John works as a C programmer. He develops the following C program:
His program is vulnerable to a __________ attack.
Show answer details
Correct answer: C
Explanation:
This program takes a user-supplied string and copies it into 'buffer1', which can hold up to 10 bytes of data. If a user sends more than 10 bytes, it would result in a buffer overflow. - 7
Fill in the blank with the appropriate term. ________________________ is the complete network configuration and information toolkit that uses multi-threaded and multi-connection technologies in order to be very fast and efficient.
Show answer details
Correct answer: A
NetRanger is the complete network configuration and information toolkit that includes the following tools: a Ping tool, Trace Route tool, Host Lookup tool, Internet time synchronizer, Whois tool, Finger Unix hosts tool, Host and port scanning tool, check multiple POP3 mail accounts tool, manage dialup connections tool, Quote of the day tool, and monitor Network Settings tool. These tools are integrated in order to use an application interface with full online help. NetRanger is designed for both new and experienced users. This tool is used to help diagnose network problems and to get information about users, hosts, and networks on the Internet or on a user computer network. NetRanger uses multi-threaded and multi-connection technologies in order to be very fast and efficient.
- 8
Fill in the blank with the appropriate term. A _______________device is used for uniquely recognizing humans based upon one or more intrinsic physical or behavioral traits.
Show answer details
Correct answer: A
Explanation:
A biometric device is used for uniquely recognizing humans based upon one or more intrinsic, physical, or behavioral traits.
Biometrics is used as a form of identity access management and access control. It is also used to identify individuals in groups that are under surveillance. Biometric characteristics can be divided into two main classes:- Physiological: These devices are related to the shape of the body. These are not limited to the fingerprint, face recognition, DNA, hand and palm geometry, and iris recognition, which has largely replaced the retina and odor/scent.
- Behavioral: These are related to the behavior of a person. They are not limited to the typing rhythm, gait, and voice.
- 9
Which of the following analyzes network traffic to trace specific transactions and can intercept and log traffic passing over a digital network? Each correct answer represents a complete solution.
Choose all that apply.Show answer details
Correct answer: A, C
A, C -- Explanation:
Protocol analyzer (also known as a network analyzer, packet analyzer or sniffer, or for particular types of networks, an Ethernet sniffer or wireless sniffer) is computer software or computer hardware that can intercept and log traffic passing over a digital network. As data streams flow across the network, the sniffer captures each packet and, if needed, decodes and analyzes its content according to the appropriate RFC or other specifications.
Answer option D is incorrect. Performance Monitor is used to get statistical information about the hardware and software components of a server.
Answer option B is incorrect. A spectrum analyzer, or spectral analyzer, is a device that is used to examine the spectral composition of an electrical, acoustic, or optical waveform. It may also measure the power spectrum.A, C -- Explanation:
Protocol analyzer (also known as a network analyzer, packet analyzer or sniffer, or for particular types of networks, an Ethernet sniffer or wireless sniffer) is computer software or computer hardware that can intercept and log traffic passing over a digital network. As data streams flow across the network, the sniffer captures each packet and, if needed, decodes and analyzes its content according to the appropriate RFC or other specifications.
Answer option D is incorrect. Performance Monitor is used to get statistical information about the hardware and software components of a server.
Answer option B is incorrect. A spectrum analyzer, or spectral analyzer, is a device that is used to examine the spectral composition of an electrical, acoustic, or optical waveform. It may also measure the power spectrum.
