HPE6-A84 Aruba Network Security Expert Practice Questions
Prepare for HPE6-A84 with more than an answer.
- Exam fee
- $400 USD
- Level
- Expert
- Valid for
- 3 years
Domains covered on the exam 5
- Protect and Defend - Security Foundation25%
- Protect and Defend - Secure Unified Infrastructure25%
- Protect and Defend - Secure the WAN8%
- Analyze - Threat Detection and Remediation38%
- Investigate - Comprehensive Threat Analysis4%
- 1
A university is deploying Eduroam and needs to proxy authentication requests for visiting students to their home institutions. Which configuration on the university's ClearPass server is required to forward these RADIUS requests based on the realm (e.g., @other-uni.edu)?
Show answer details
Correct answer: D
To forward RADIUS requests, you use a RADIUS Proxy Service (or a standard service with a Proxy Profile). The Service Rule typically inspects the User-Name attribute for a specific realm (using 'Ends With' or regex) and routes the request to the defined Proxy Target (the upstream federation servers).
- 2
You are auditing the security of an Aruba Mobility Controller. You notice that the 'logon' role is configured with the following ACL:
'user any udp 68 deny'
'any any svc-dhcp permit'
'user any svc-dns permit'
'user any svc-http-accl permit'
'user any svc-https-accl permit'Why is the first rule 'user any udp 68 deny' potentially problematic for a Captive Portal workflow?
Show answer details
Correct answer: C
DHCP client traffic originates from UDP port 68. If the first rule denies traffic from 'user' (the client) with source/destination port 68 (depending on how the rule is interpreted, typically 'udp 68' implies destination, but if it matches the protocol/port logic for DHCP incorrectly or if it blocks the return), it can break IP acquisition. However, specifically, 'user any udp 68 deny' would block the client sending to port 68. DHCP requests go to port 67. But often 'logon' roles need to explicitly PERMIT dhcp. The issue here is likely that the explicit deny might interfere if the client tries to renew or if the rule syntax matches the client port.
- 3
Select TWO reasons why an administrator might choose to implement 'MAC-Auth' BEFORE '802.1X' in the authentication priority list on a switch port. (Select TWO)
Show answer details
Correct answer: A, D
If 802.1X is first, the switch waits for EAP timeouts before trying MAC Auth. For a network with many printers/IoT devices, putting MAC Auth first allows them to authenticate immediately without the EAP timeout delay.
In MAC Caching (for guests), the device is registered after the first login. On subsequent connections, the device authenticates via MAC Auth. If 802.1X were first, the guest device (which doesn't have 802.1X configured) would fail EAP, then hit MAC Auth. However, some admins prefer MAC Auth first to immediately catch these cached guests.
- 4
A customer wants to use ClearPass to assign unique VLANs to users based on their Active Directory 'Department' attribute. The switch supports RFC 4675 (RADIUS Attributes for VLAN assignment). Which three RADIUS attributes must be returned in the Enforcement Profile to assign the user to VLAN 20 named 'Finance'? (Select THREE)
Show answer details
Correct answer: C, D, E
This attribute carries the actual VLAN ID (e.g., '20') or Name.
Required part of the standard triplet for VLAN assignment.
RFC 4675/3580 requires three attributes for VLAN assignment: Tunnel-Type (13) set to VLAN, Tunnel-Medium-Type (6) set to IEEE-802 (6), and Tunnel-Private-Group-ID (81) set to the VLAN ID or Name.
- 5
True or False: In a ClearPass Policy Manager 'Service' configuration, the 'Authorization' tab allows you to fetch additional attributes from external databases (like SQL or AD) after the initial authentication has succeeded, to be used in Policy enforcement.
Show answer details
Correct answer: A
This is the primary purpose of the Authorization tab. While Authentication verifies identity, Authorization sources are queried (typically using the username) to retrieve group memberships, department info, or custom attributes that are then used in the Enforcement Policy conditions.
- 6
You are designing an Aruba ClearPass Policy Manager (CPPM) solution for a customer. You learn that the customer has a Palo Alto firewall that filters traffic between clients in the campus and the data center.Which integration can you suggest? A.Sending Syslogs from the firewall to CPPM to signal CPPM to change the authentication status for misbehaving clientsB.Importing clients’ MAC addresses to configure known clients for MAC authentication more quicklyC.Establishing a double layer of authentication at both the campus edge and the data center DMZD.Importing the firewall's rules to program downloadable user roles for AOS-CX switches more quickly
Show answer details
Correct answer: A
- 7
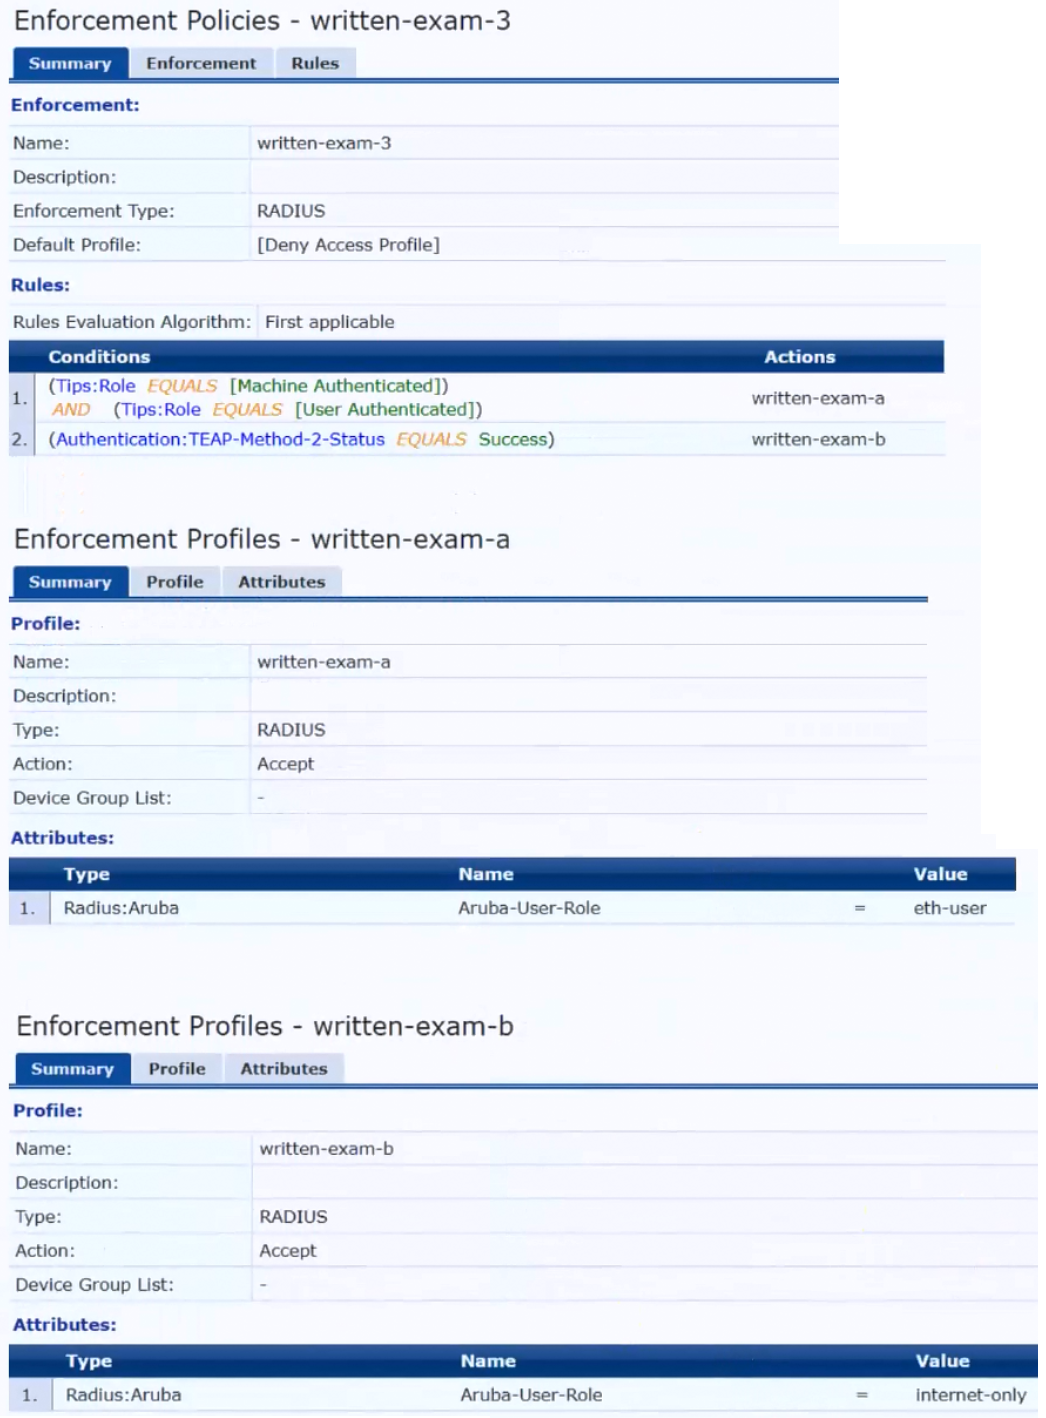
Refer to the scenario.A customer has an Aruba ClearPass cluster. The customer has AOS-CX switches that implement 802.1X authentication to ClearPass Policy Manager (CPPM).Switches are using local port-access policies.The customer wants to start tunneling wired clients that pass user authentication only to an Aruba gateway cluster. The gateway cluster should assign these clients to the “eth-internet" role. The gateway should also handle assigning clients to their VLAN, which is VLAN 20.The plan for the enforcement policy and profiles is shown below:The gateway cluster has two gateways with these IP addresses:• Gateway 1o VLAN 4085 (system IP) = 10.20.4.21o VLAN 20 (users) = 10.20.20.1o VLAN 4094 (WAN) = 198.51.100.14• Gateway 2o VLAN 4085 (system IP) = 10.20.4.22o VLAN 20 (users) = 10.20.20.2o VLAN 4094 (WAN) = 198.51.100.12• VRRP on VLAN 20 = 10.20.20.254The customer requires high availability for the tunnels between the switches and the gateway cluster. If one gateway falls, the other gateway should take over its tunnels. Also, the switch should be able to discover the gateway cluster regardless of whether one of the gateways is in the cluster.You are setting up the UBT zone on an AOS-CX switch.Which IP addresses should you define in the zone? A.Primary controller = 10.20.4.21; backup controller = 10.20.4.22B.Primary controller = 198.51.100.14; backup controller = 10.20.4.21C.Primary controller = 10.20.4.21; backup controller, not definedD.Primary controller = 10.20.20.254; backup controller, not defined
Show answer details
Correct answer: A
- 8
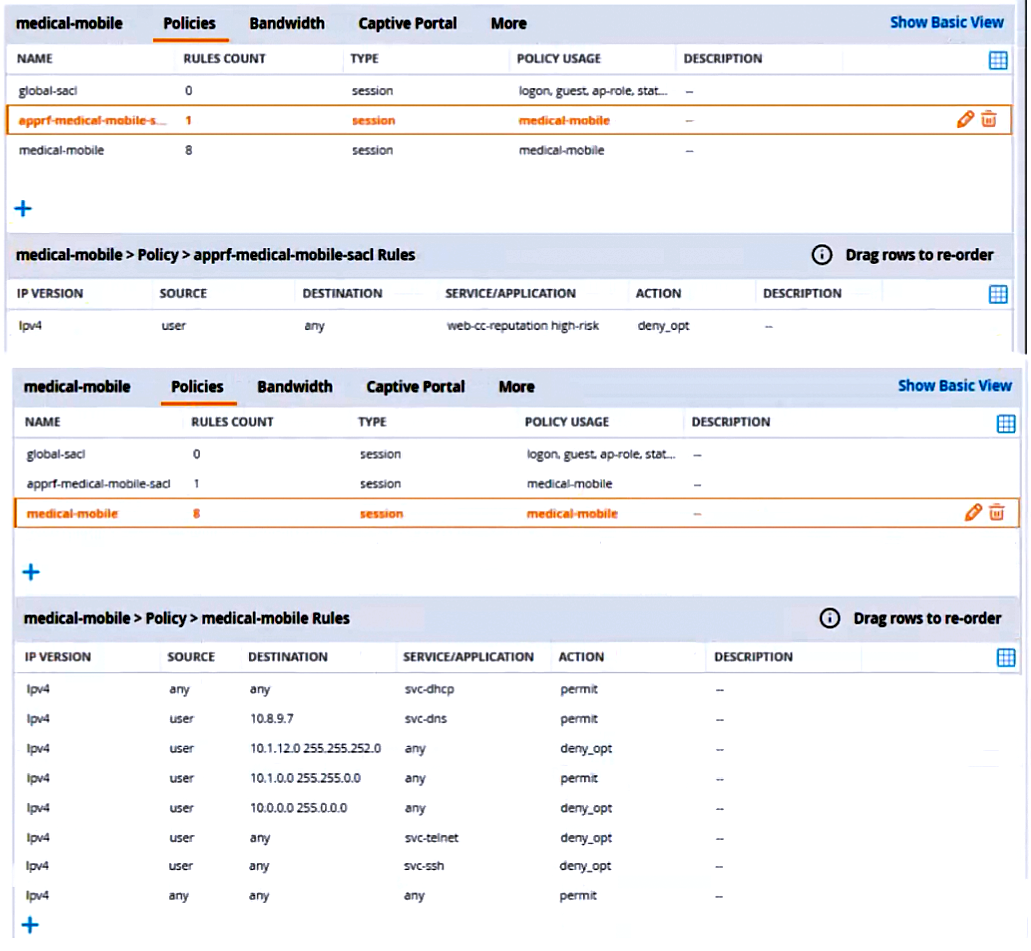
Refer to the scenario.A customer requires these rights for clients in the “medical-mobile” AOS firewall role on Aruba Mobility Controllers (MCs):Permitted to receive IP addresses with DHCPPermitted access to DNS services from 10.8.9.7 and no other serverPermitted access to all subnets in the 10.1.0.0/16 range except denied access to 10.1.12.0/22Denied access to other 10.0.0.0/8 subnetsPermitted access to the InternetDenied access to the WLAN for a period of time if they send any SSH trafficDenied access to the WLAN for a period of time if they send any Telnet trafficDenied access to all high-risk websitesExternal devices should not be permitted to initiate sessions with “medical-mobile” clients, only send return traffic.The exhibits below show the configuration for the role.There are multiple issues with this configuration. What is one change you must make to meet the scenario requirements? (In the options, rules in a policy are referenced from top to bottom. For example, “medical-mobile” rule 1 is “ipv4 any any svc-dhcp permit,” and rule 8 is “ipv4 any any any permit”.) A.In the “medical-mobile” policy, move rules 2 and 3 between rules 7 and 8.B.In the “medical-mobile” policy, change the subnet mask in rule 3 to 255.255.248.0.C.Move the rule in the “apprf-medical-mobile-sacl” policy between rules 7 and 8 in the “medical-mobile” policy.D.In the “medical-mobile” policy, change the source in rule 8 to “user.”
Show answer details
Correct answer: B
