JN0-635 Security, Professional (JNCIP-SEC) Practice Questions
Prepare for JN0-635 with more than an answer.
- Exam fee
- $400 USD
- Level
- Professional
- Valid for
- 3 years
Domains covered on the exam 8
- Troubleshooting Security Policies and Security Zones12%
- Logical Systems and Tenant Systems15%
- Layer 2 Security14%
- Advanced Network Address Translation (NAT)13%
- Advanced IPsec VPNs20%
- Advanced Policy-Based Routing (APBR)10%
- Multinode High Availability (HA)12%
- Automated Threat Mitigation4%
- 1
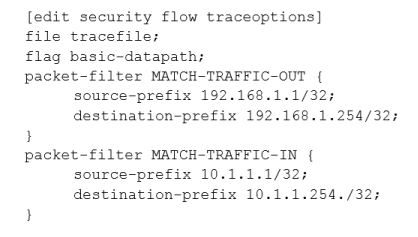
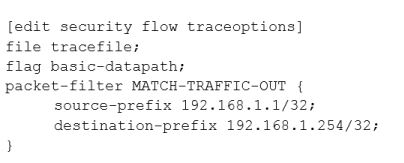
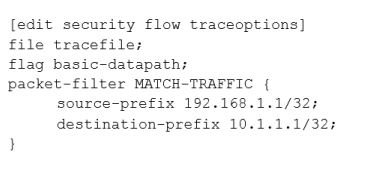
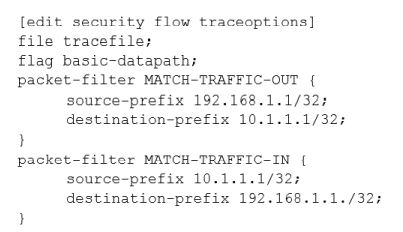
Click the Exhibit button.
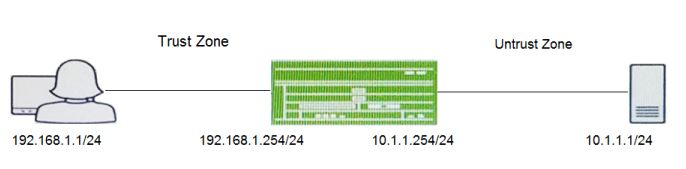
A user reports trouble when using SSH to a server outside your organization. The traffic traverses an SRX Series device that is performing NAT and applying security policies.
Referring to the exhibit, which configuration will allow you to see the bidirectional flow through the SRX Series device?
Show answer details
Correct answer: D
D
- 2
You configured a security policy permitting traffic from the trust zone to the DMZ zone, inserted the new policy at the top of the list, and successfully committed it to the SRX Series device. Upon monitoring, you notice that the hit count does not increase on the newly configured policy.
In this scenario, which two commands would help you to identify the problem? (Choose two.)
Show answer details
Correct answer: B, D
B, D -- Reference: https://www.iuniper.net/documentation/en US/iunos/topics/topic-map/monitoring-troubleshooting-security-policy.html
B, D -- Reference: https://www.iuniper.net/documentation/en US/iunos/topics/topic-map/monitoring-troubleshooting-security-policy.html
- 3
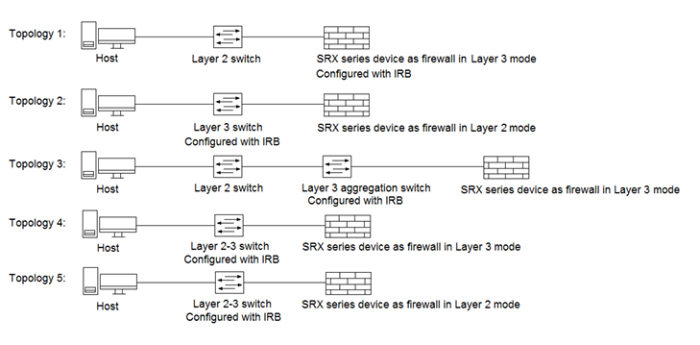
Click the Exhibit button.
Referring to the exhibit, which three topologies are supported by Policy Enforcer? (Choose three.)
Show answer details
Correct answer: A, D, E
A, D, E -- Reference: https://www.juniper.net/documentation/en US/junos-space17.2/policy-enforcer/topics/concept/policy-enforcer-deployment-supported-topologies.html
A, D, E -- Reference: https://www.juniper.net/documentation/en US/junos-space17.2/policy-enforcer/topics/concept/policy-enforcer-deployment-supported-topologies.html
A, D, E -- Reference: https://www.juniper.net/documentation/en US/junos-space17.2/policy-enforcer/topics/concept/policy-enforcer-deployment-supported-topologies.html
- 4
Malware that is detonated by the JATP sandbox must be able to communicate with the Internet without being able to harm your local network resources.
Which statement is correct in this scenario?
Show answer details
Correct answer: A
Reference: https://www.juniper.net/documentation/en US/release-independent/jatp/topics/topic-map/jatp-getting-started.html
- 5
Click the Exhibit button.
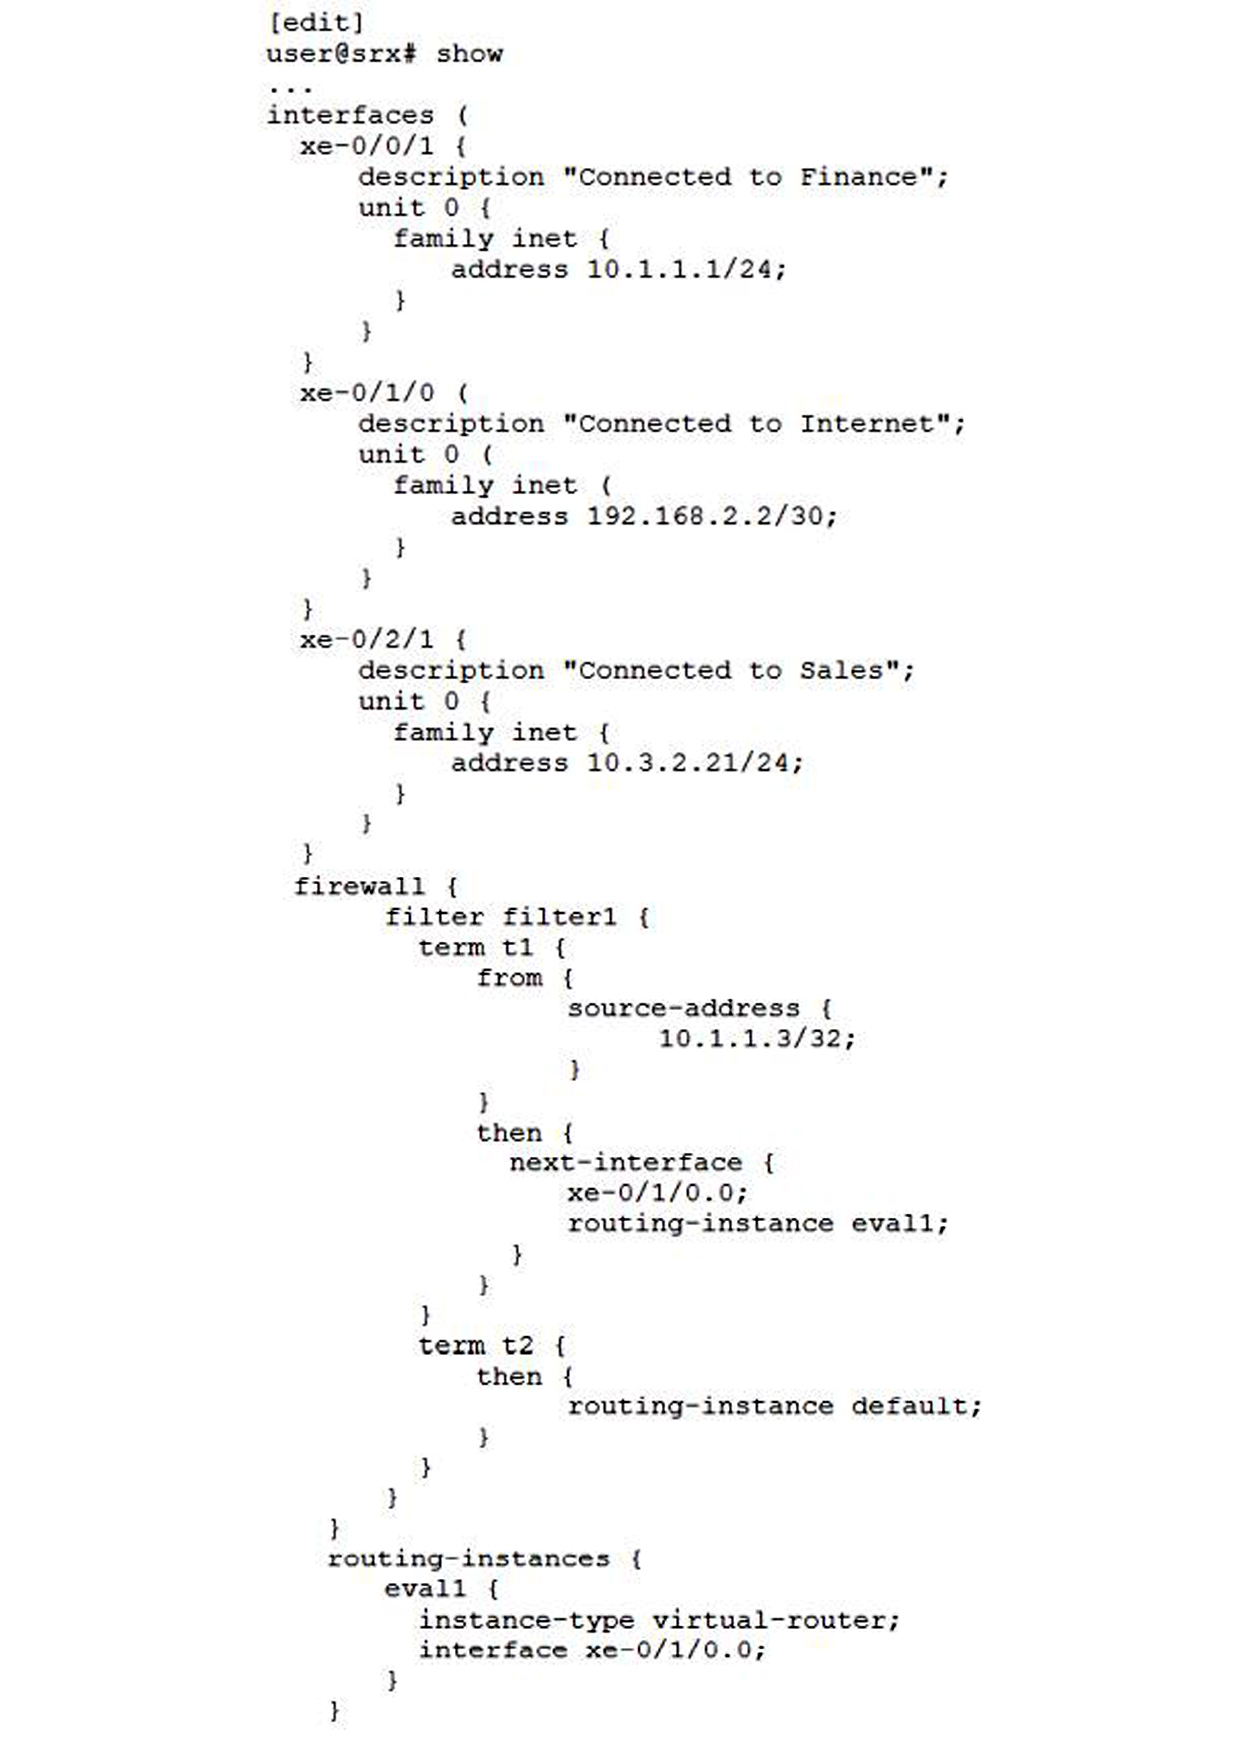
You are asked to look at a configuration that is designed to take all traffic with a specific source IP address and forward the traffic to a traffic analysis server for further evaluation. The configuration is not working as intended.
Referring to the exhibit, which change must be made to correct the configuration?
Show answer details
Correct answer: C
C
- 6
Click the Exhibit button.
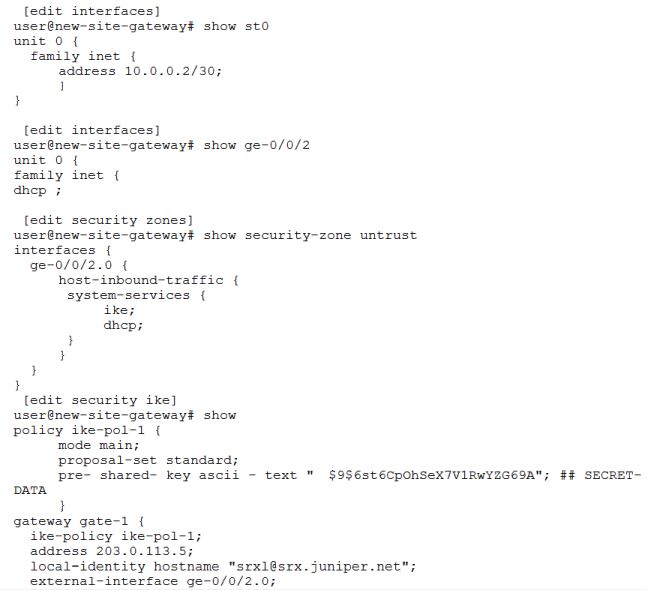
Your company has purchased a competitor and now must connect the new network to the existing one. The competitor’s gateway device is receiving its ISP address using DHCP. Communication between the two sites must be secured; however, obtaining a static public IP address for the new site gateway is not an option at this time. The company has several requirements for this solution:
• A site-to-site IPsec VPN must be used to secure traffic between the two sites;
• The IKE identity on the new site gateway device must use the hostname option; and
• Internet traffic from each site should exit through its local Internet connection.The configuration shown in the exhibit has been applied to the new site’s SRX, but the secure tunnel is not working.
In this scenario, what configuration change is needed for the tunnel to come up?
Show answer details
Correct answer: A
A