SecurityX Practice Questions
Prepare for CAS-005 with more than an answer.
Unlock the full exam and previous versions
- v1Version 1 210 questions Current
- CA1-005Legacy CompTIA SecurityX (Extended) 215 questions Locked
- CAS-003Legacy CompTIA Advanced Security Practitioner (CASP) 361 questions Locked
- CAS-004Legacy Comptia Advanced Security Practitioner (casp+) 149 questions Locked
- Exam fee
- $509 USD
- Level
- Expert
- Valid for
- 3 years
Domains covered on the exam 4
- Governance, Risk, and Compliance20%
- Security Architecture27%
- Security Engineering31%
- Security Operations22%
- 1
A security architect is designing a high-availability solution for a stateful web application hosted in a single AWS region. To protect against the failure of an entire Availability Zone (AZ), the architect plans to use an Application Load Balancer (ALB) distributing traffic across EC2 instances in multiple AZs. What additional component is essential to ensure user sessions are maintained seamlessly if an AZ fails?
Show answer details
Correct answer: B
For a stateful application to survive an AZ failure, the session state cannot be stored locally on the EC2 instances. If an instance fails, its session data is lost. Sticky sessions would also fail because the target instance would be gone. The correct architectural pattern is to externalize the session state into a replicated, highly available service like Amazon ElastiCache for Redis. This allows any EC2 instance in any available AZ to retrieve the session data and continue the user's session seamlessly.
- 2
True or False: In a scenario where an organization implements homomorphic encryption for processing sensitive data in a public cloud, the cloud provider's administrators can still view the plaintext data if they have root access to the underlying virtual machine hosts.
Show answer details
Correct answer: B
The statement is false. The fundamental principle of homomorphic encryption is that it allows computations to be performed on ciphertext, generating an encrypted result which, when decrypted, matches the result of the operations as if they had been performed on the plaintext. At no point during processing is the data decrypted on the cloud provider's infrastructure. Therefore, even with root access, the cloud provider cannot view the plaintext data.
- 3
A security architect is reviewing the design of a new Secure Access Service Edge (SASE) implementation. The design combines SD-WAN capabilities with several cloud-native security functions. To ensure the architecture adheres to the core principles of SASE, which of the following is the most critical design consideration?
Show answer details
Correct answer: B
The core principle of SASE is the convergence of networking (like SD-WAN) and security functions (like SWG, CASB, ZTNA, FWaaS) into a unified, cloud-native service. This model moves policy enforcement from the traditional datacenter to the cloud edge, closer to users and devices. Backhauling traffic to a central datacenter is the opposite of the SASE model. While vendor diversity and cost are factors, the architectural convergence is the defining characteristic.
- 4
A company is developing a new IoT device that will be deployed in unsecured environments. The device needs to prove its boot process has not been tampered with before it is allowed to connect to the cloud management platform. The security architect has specified that the device must use a TPM 2.0 chip. What TPM feature allows the cloud platform to cryptographically verify the integrity of the entire boot sequence, including firmware, bootloader, and OS kernel?
Show answer details
Correct answer: C
Remote Attestation is the process by which a remote system (the cloud platform) can verify the integrity of a client's (the IoT device's) boot process. This is achieved through a process called Measured Boot, where the TPM measures (hashes) each component of the boot sequence and stores the values in Platform Configuration Registers (PCRs). During attestation, the TPM generates a signed quote of these PCR values using a unique Attestation Identity Key (AIK). The cloud platform can then validate this signature and compare the PCR values to a known-good baseline to verify the device's integrity.
- 5
A SOC analyst is investigating an alert from a User and Entity Behavior Analytics (UEBA) system. The alert indicates that a user account belonging to a remote salesperson has accessed the corporate finance database for the first time, from an unfamiliar IP address, and attempted to download a large volume of data outside of normal business hours. The UEBA system has assigned a high risk score to this activity. This is an example of the UEBA system detecting anomalies based on which primary principle?
graph LR subgraph Baseline["User's Normal Behavior"] A[Accesses CRM] B[Connects from US IP] C[Works 9am-5pm] D[Low data download] end subgraph Anomaly["Anomalous Activity"] E[Accesses Finance DB] F[Connects from DE IP] G[Works at 2am] H[High data download] end Baseline -- Deviates from --> AnomalyShow answer details
Correct answer: C
UEBA systems work by creating a baseline of normal behavior for each user and entity over time. This includes typical login times, locations, data access patterns, and systems used. The alert was triggered because the observed activity (accessing finance DB, new IP, off-hours, large download) was a significant deviation from the salesperson's established behavioral baseline. The system flagged this combination of anomalies as high-risk.
- 6
A security engineer is reviewing event logs because an employee successfully connected a personal Windows laptop to the corporate network, which is against company policy. Company policy allows all Windows 10 and 11 laptops to connect to the system as long as the MDM agent installed by IT is running. Only compliant devices can connect, and the logic in the system to evaluate compliant laptops is as follows:Which of the following most likely occurred when the employee connected a personally owned Windows laptop and was allowed on the network?
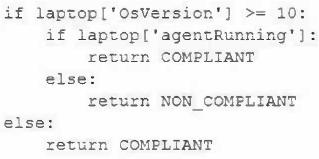
Show answer details
Correct answer: B
- 7
An organization is working to secure its development process to ensure developers cannot deploy artifacts directly into the production environment. Which of the following security practice recommendations would be the best to accomplish this objective?
Show answer details
Correct answer: C
- 8
A security architect discovers the following while reviewing code for a company's website: selection = "SELECT Item FROM Catalog WHERE ItemID = " & Request("ItemID")Which of the following should the security architect recommend?
Show answer details
Correct answer: B
- 9
A security architect needs to enable a container orchestrator for DevSecOps and SOAR initiatives. The engineer has discovered that several Ansible YAML files used for the automation of configuration management have the following content:Which of the following should the engineer do to correct the security issues presented within this content?
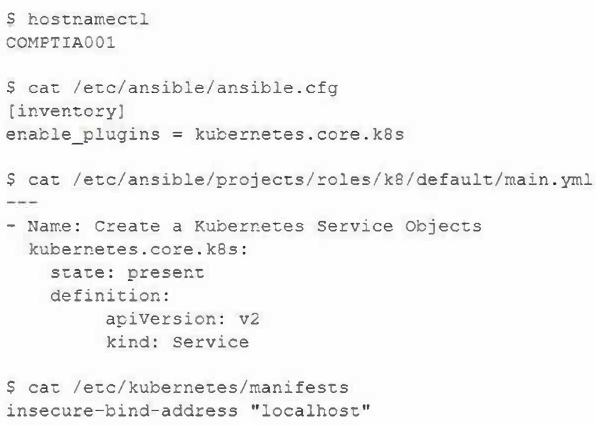
Show answer details
Correct answer: E
- 10
A CRM company leverages a CSP PaaS service to host and publish Its SaaS product. Recently, a large customer requested that all infrastructure components must meet strict regulatory requirements, including configuration management, patch management, and life-cycle management. Which of the following organizations is responsible for ensuring those regulatory requirements are met?
Show answer details
Correct answer: A
